What changed on 16 September 2026
Article 184 of Decree-Law 6/2025 gave in-scope entities one year to regularise their status under the new Central Bank law. That year is over. Three things follow for a continuity function.
- The question moved from «are you preparing» to «show me». An examination now expects dated evidence: a signed BCM policy, a BIA refreshed within the year, a plan, the last test report with timings and findings, closed actions and board minutes. The CBUAE checklist lists the documents in the order an examiner asks for them.
- Insurers, payment providers and technology enablers are in the same room as banks. The consolidated law brought them under one supervisor; proportionality scales the size of the system, not the obligation to have one.
- Extensions are discretionary and individual. CBUAE may extend for a named entity on request. A general extension was not granted, and an entity that has not asked is simply late. The timeline shows what a realistic catch-up plan looks like from here.
The two layers you are regulated by
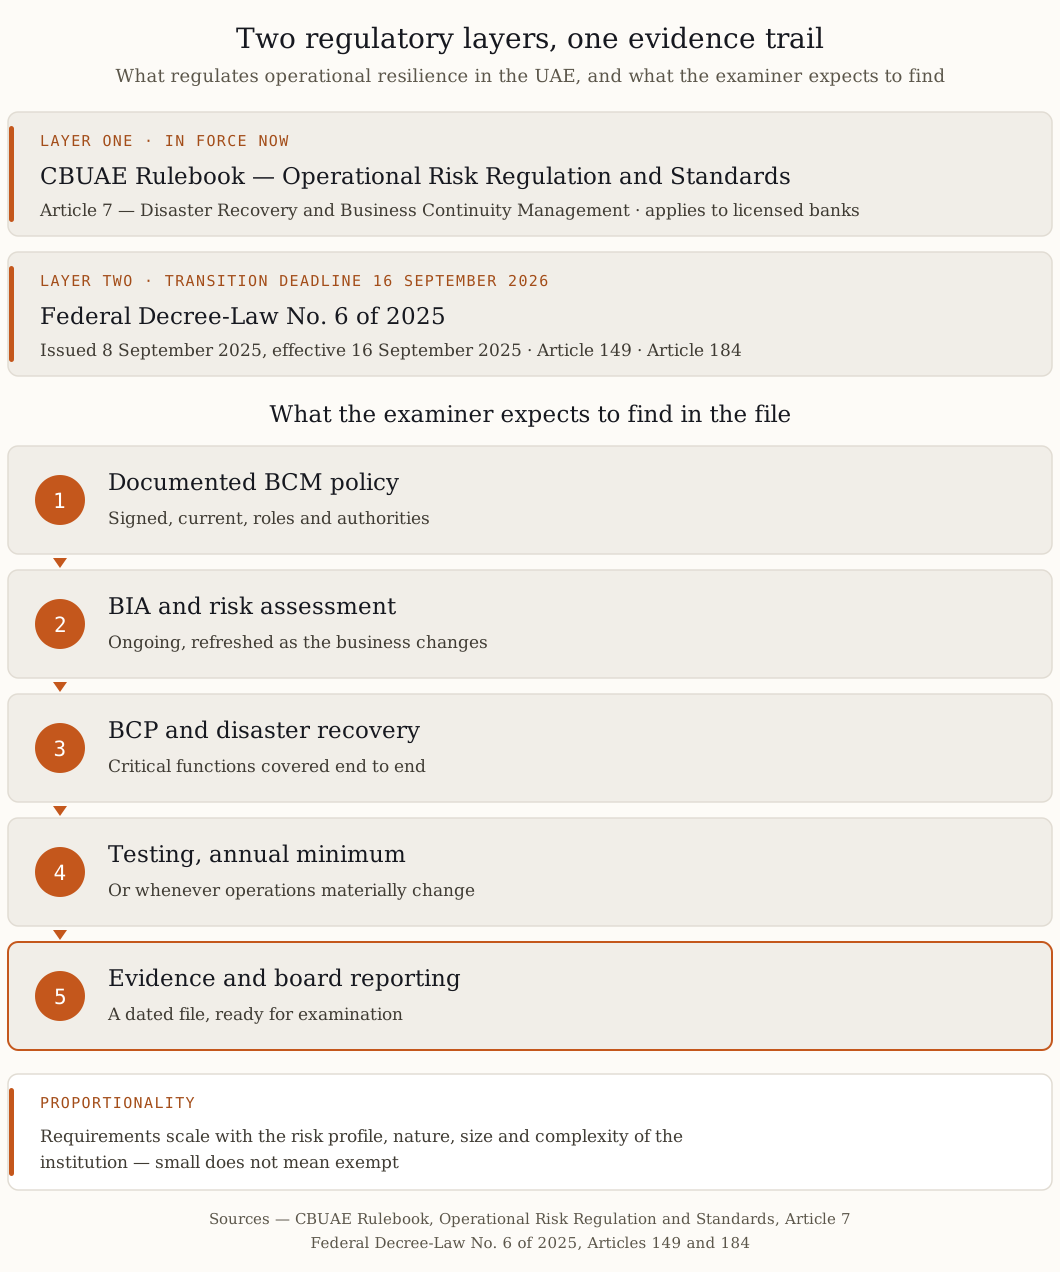
Layer one: the CBUAE Rulebook. The Operational Risk Regulation and Standards apply to licensed banks and set explicit requirements for business continuity. Article 7 — Disaster Recovery and Business Continuity Management — is the operative text: a documented BCM policy with roles and authorities, ongoing business impact analysis and risk assessment, a documented business continuity plan, and testing at least annually or whenever operations materially change. The requirements scale with the risk profile, nature, size and complexity of the institution.
Layer two: the new Central Bank law. Federal Decree-Law No. 6 of 2025, issued on 8 September 2025 and effective from 16 September 2025, replaced the 2018 Central Bank law and the 2023 insurance law in one consolidated framework. It broadens who is in scope — banks, insurers, payment providers and technology enablers — reinforces supervision and examination powers, and (Article 149) mandates fraud prevention mechanisms and prompt customer notification of security breaches.
Article 184 gives in-scope entities a one-year transitional period — until 16 September 2026 — to regularise their status under the new law. That date is the anchor of the regulatory year. See our countdown plan.
What Article 7 requires, in practice
| Requirement | What the supervisor expects to see |
|---|---|
| Documented BCM policy | Objectives, approach, and named roles with authority to act — signed, current, known to the people in it |
| BIA and risk assessment, ongoing | Critical business functions identified, disruption impact assessed over time — refreshed, not a 2022 artefact |
| Documented BCP | A plan that meets the policy's objectives and covers critical functions end to end |
| Annual testing minimum | Evidence that staff can execute contingency plans and that recovery objectives and timeframes are actually met |
| Disaster recovery | Technology recovery arrangements that limit losses in severe disruption |
| Proportionality | Arrangements commensurate with your size and complexity — small does not mean exempt, it means right-sized |
Two failure patterns dominate supervisory findings across the region. First, testing that proves nothing: a tabletop walkthrough with no findings, no timings, no evidence recovery objectives were met. Second, BIA as an archive: impact analysis done once, while the business changed underneath it. Both are visible to an examiner within an hour.
Who is in scope
- Banks — the full Rulebook operational risk framework applies, including Article 7.
- Insurers — consolidated under the new law; resilience expectations follow supervision.
- Payment providers and fintech / technology enablers — newly consolidated in the 2025 framework; if you are in the transaction chain, resilience questions reach you.
- Critical suppliers to all of the above — outsourcing oversight makes your continuity part of your client's compliance file.
A pragmatic compliance path
- 1 · Gap assessment against Article 7 and resilience expectations, starting from the CBUAE checklist. 2-3 weeks, every gap priced in downtime and finding-risk terms.
- 2 · Refresh the BIA. Critical functions, impact over time, recovery objectives your current arrangements can really meet.
- 3 · Fix the plan, not the binder. First-hours authority, communication trees, workarounds, technology recovery — short and executable.
- 4 · Test like an examiner. A realistic scenario, timed, with findings and closed actions. This single artefact answers most supervisory questions.
- 5 · Report to the board. Resilience metrics the board sees monthly — see our board reporting guide.
Impact tolerance: how to set it and how to measure it
Impact tolerance is the maximum level of disruption to an important business service that the institution is prepared to accept, expressed as a measurable limit rather than as an adjective. It is the operational resilience regulators' central instrument, and the point where most first drafts fail: they state a recovery time and call it a tolerance.
A tolerance has four parts. The service, defined from the customer's side, not the department's: «retail customers can make outgoing payments», not «the payments platform». The metric on which the limit is set: time, but also volume, value or number of customers affected. The limit itself, with the arithmetic that justifies it. And the severe but plausible scenario against which the limit is tested.
A worked example. Service: outgoing retail payments. Tolerance: no more than 4 hours of full outage on a business day, and no more than 2 per cent of daily payment value failed or delayed beyond the day, before harm to customers and to market integrity becomes intolerable. Justification: after 4 hours salary and rent instructions start missing cut-off times across the customer base, which the institution judges intolerable; the 2 per cent value limit comes from the settlement position the institution can cover without external funding. Test: a scenario in which the core payments engine is lost at 09:00 on a month-end day; the last exercise restored the service in 3 hours 20 minutes and delayed 0.8 per cent of value, so the service currently sits inside tolerance, with the margin recorded.
Three checks before a tolerance goes to the board. It is set per service, not per system. It can be breached, and the institution knows how it would find out. And the last test result is stated next to it, so the board sees the distance between the limit and reality, not only the limit. How this is reported quarter by quarter is in the board reporting guide.
Frequently asked questions
What exactly changes on 16 September 2026?
Article 184 of Decree-Law 6/2025 ends the one-year transitional period: entities newly in scope or required to make changes must have regularised licensing and compliance by that date, subject to CBUAE discretion to extend. Waiting for an extension is not a strategy.
We are a small institution. Do the BCM requirements really apply?
Yes — proportionally. The Rulebook explicitly scales requirements to the risk profile, nature, size and complexity of the business. A small institution needs a smaller, but still real and tested, system.
How does this relate to NCEMA 7000?
NCEMA 7000 is the national BCM standard; CBUAE requirements are sector regulation for financial institutions. The disciplines overlap heavily — one well-built BCM system, properly documented, serves both. See our NCEMA 7000 guide.
What evidence should we have ready for an examination?
The signed BCM policy, current BIA outputs, the BCP, the last test report with timings and findings, closed-action records, and board reporting on resilience. Dated documents; interviews will verify people know their roles.
Sources: CBUAE Rulebook — Operational Risk Regulation and Standards, Article 7 (Disaster Recovery and Business Continuity Management), rulebook.centralbank.ae · Federal Decree-Law No. 6 of 2025 (issued 8 September 2025), uaelegislation.gov.ae · legal analyses by White & Case, Addleshaw Goddard, Ashurst, 2025.